


Content Security Policy
Content Security Policy: Securing Modern Web Applications

- Preventing clickjacking by controlling the embedding of web pages.
- Regulatory compliance : Supports adherence to industry standards and legal requirements for protecting sensitive information. [3]
- Adaptability : CSP can be updated promptly to counter emerging threats as the security environment changes. [1]
- Compatibility issues : Overly restrictive policies may inadvertently block legitimate content, disrupting website functionality. [3]
- Maintenance : Regular updates to the policy are necessary as website structure and third-party dependencies evolve.
- Best practices suggest rolling out CSP incrementally, with ongoing testing and thorough documentation to ensure both robust security and a positive user experience. [3]
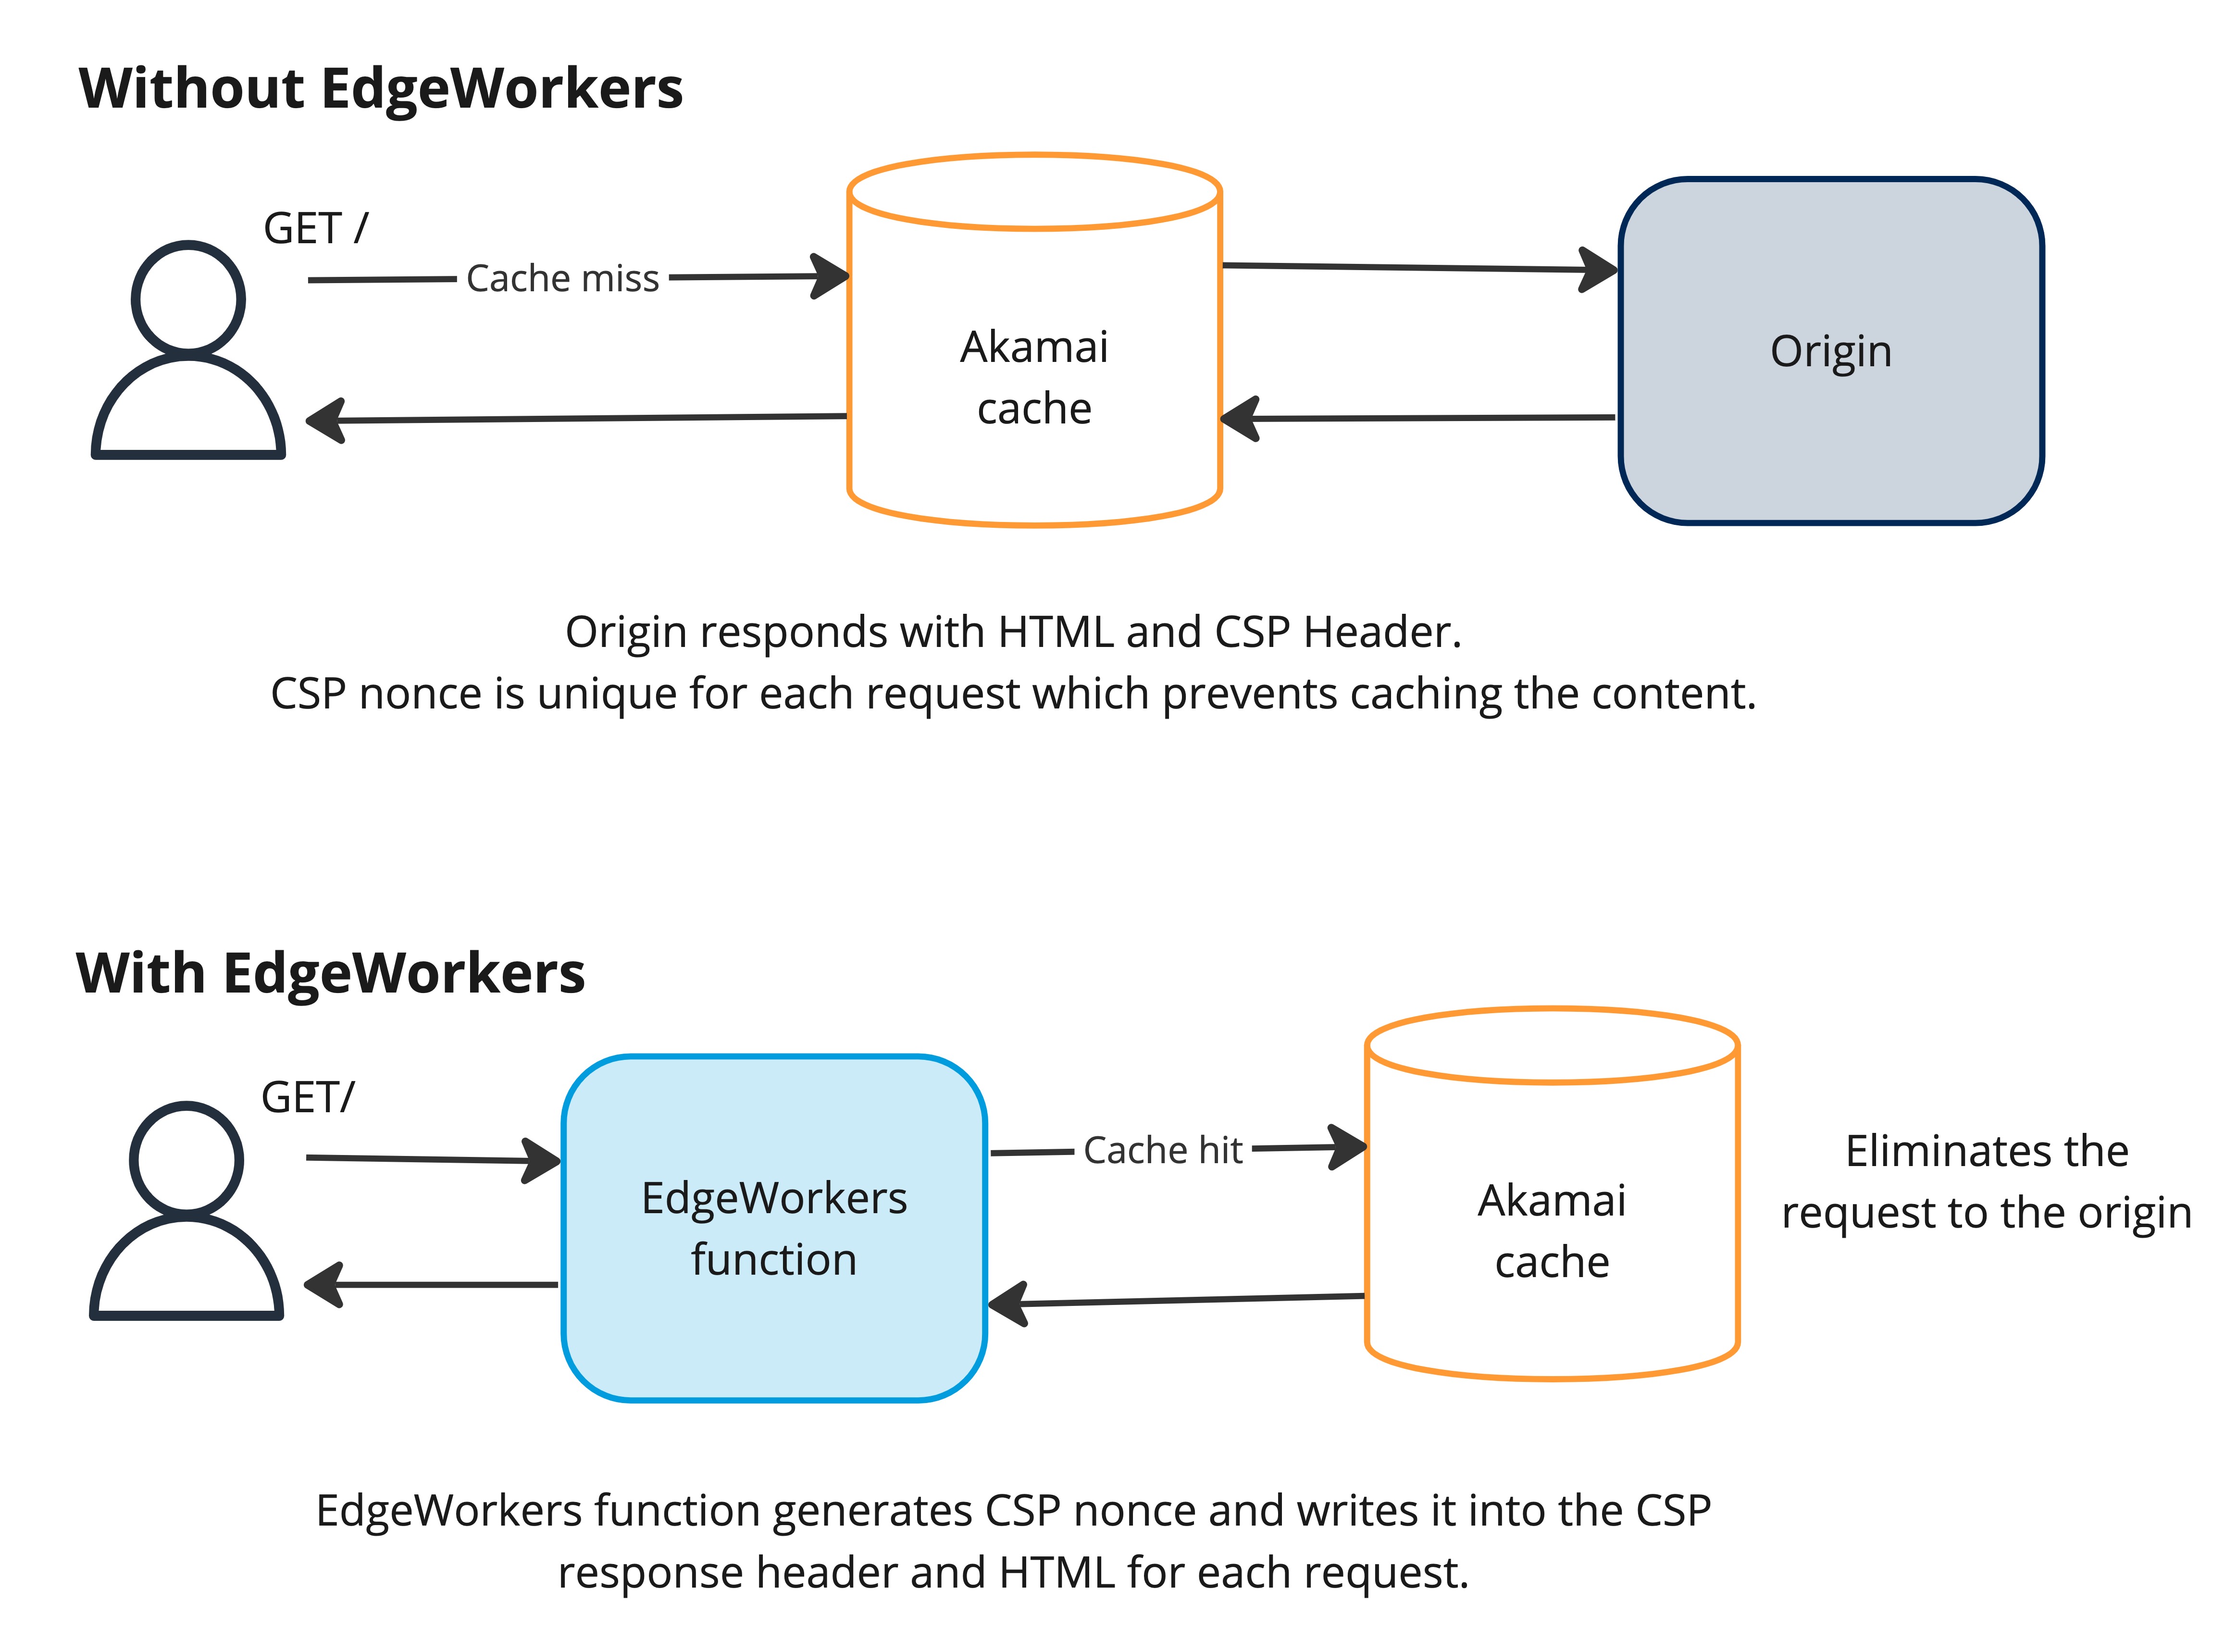
- Integration of CSP with other security headers for layered protection.
- Automation tools that facilitate policy creation, validation, and maintenance.
- Real-time analytics for policy violation reporting and faster incident response.
Citations
[1] 2025, Oct 28. Content Security Policies (CSP): Implementation and Benefits - Verpex . Published: 2024-12-23 | Updated: 2025-10-28
[2] 2025, Nov 08. Content Security Policy (CSP) - Jscrambler . Published: 2004-01-01 | Updated: 2025-11-08
[3] 2025, Sep 05. Why Content Security Policy (CSP) Implementation is a Must for ... . Published: 2024-08-28 | Updated: 2025-09-05
[4] 2025, Nov 14. Content security policy | Web Security Academy - PortSwigger . Updated: 2025-11-14
[5] 2025, Nov 14. What is Content Security Policy (CSP) | Header Examples - Imperva . Published: 2024-05-07 | Updated: 2025-11-14
[6] 2025, Nov 13. What is a Content Security Policy (CSP)? | Feroot . Published: 2025-06-18 | Updated: 2025-11-13
[7] 2025, Jul 16. What is CSP (Content-Security-Policy) and How does it Relate to Qlik? . Published: 2021-09-20 | Updated: 2025-07-16
[8] 2025, Jul 01. The Effective Guide to Creating a Content Security Policy . Published: 2025-01-01 | Updated: 2025-07-01